A Review of Ransomware Detection and Analysis Techniques
DOI:
https://doi.org/10.71229/xkpvr357Keywords:
ransomware, malware detection, static analysis, dynamic analysis, Machine learning, Network Traffic AnalysisAbstract
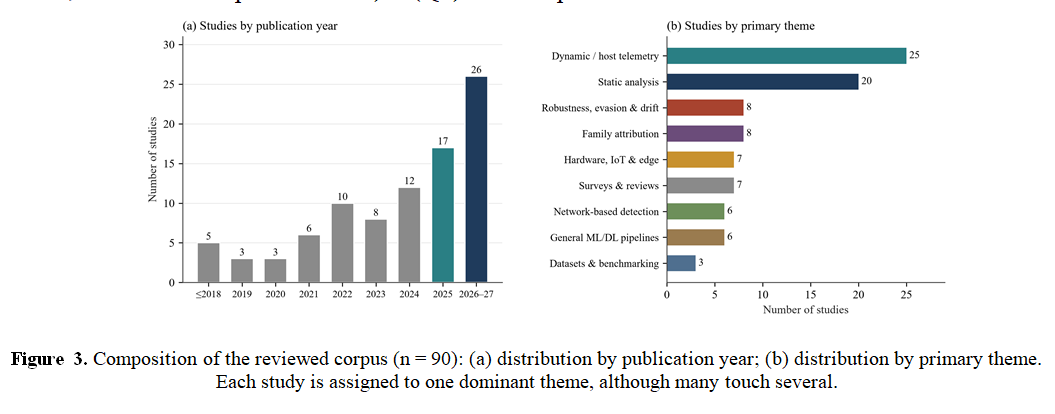
Ransomware has turned from an opportunistic nuisance into one of the most costly classes of cyber-attack, and the research effort aimed at detecting it has grown accordingly. This paper reviews that effort. Drawing on 90 unique studies published between 2013 and 2027, most of them after 2021, we organise the literature around five detection families: static file analysis, dynamic and host-telemetry analysis, deception and low-level sensing, network-based detection, and family attribution, with machine learning treated as a layer that cuts across all of them. For each family we summarise the features that are extracted, the models that are trained on them, the results that are reported and, just as importantly, the conditions under which those results were obtained. Three findings stand out. First, no single modality is sufficient: static PE-header features remain cheap and surprisingly strong for triage, but short-window behavioural telemetry is what makes interruption before bulk encryption possible, and network signals add a useful, largely independent early warning. Second, well-engineered features matter more than model depth; Random Forest and SVM remain competitive with deep networks in many settings. Third, headline accuracies above 95% coexist with fragile generalisation under packing, delayed encryption, altered I/O ordering and fileless execution, and heterogeneous datasets and protocols make cross-paper ranking unreliable. We close with a qualitative comparison of the modalities, a layered reference architecture built around disagreement-aware fusion, and a research agenda that emphasises aligned multi-modal benchmarks, family-disjoint and time-split evaluation, and deployment-level reporting.
References
[1] C. Beaman, A. Barkworth, T. D. Akande, and others, “Ransomware: Recent advances, analysis, challenges and future research directions,” Comput. Secur., 2021, doi: 10.1016/j.cose.2021.102490.
[2] L. Zhao, Z. Wang, S. Wang, and others, “Exploring the ransomware ecosystem and the active defense concept: Review of attacks and defense,” Journal of Information Security and Applications, 2025, doi: 10.1016/j.jisa.2025.104171.
[3] M. Al-Hawawreh, M. Alazab, M. A. Ferrag, and M. S. Hossain, “Securing the Industrial Internet of Things against ransomware attacks: A comprehensive analysis of the emerging threat landscape and detection mechanisms,” Journal of Network and Computer Applications, 2024, doi: 10.1016/j.jnca.2023.103809.
[4] T. R. Reshmi, “Information security breaches due to ransomware attacks – A systematic literature review,” International Journal of Information Management Data Insights, 2021, doi: 10.1016/j.jjimei.2021.100013.
[5] T. Daengsi, P. Pornpongtechavanich, P. Boonpoor, and others, “Ransomware and artificial intelligence: A comprehensive systematic review of reviews,” Bulletin of Electrical Engineering and Informatics, 2026, doi: 10.11591/eei.v15i2.11107.
[6] M. Cen, F. Jiang, X. Qin, and others, “Ransomware early detection: A survey,” Computer Networks, 2024, doi: 10.1016/j.comnet.2023.110138.
[7] X. Fang and T. Saadawi, “Artificial Intelligence-Powered Crypto Ransomware Detection,” IEEE Access, vol. 14, pp. 114776–114801, 2026, doi: 10.1109/access.2026.3710149.
[8] B. Luo, C. Guo, G.-W. Shen, and Y. Ping, “Ransomware early detection method based on API latent semantics,” Acta Electronica Sinica, 2024, doi: 10.12263/DZXB.20231039.
[9] V. Varshit, A. Roy, S. Manchanda, and R. Nithya Paranthaman, “Adaptive monitoring for early stage ransomware detection via behaviour and network traffic analysis,” in Proc. Int. Conf. Signal, Systems, and Computing for Next-Gen Automation (ICSSCNA), 2026. doi: 10.1109/ICSSCNA68616.2026.11546929.
[10] T. N. Kim, S. D. Trung, and N. M. N. Pham, “PE-MILCon: Multiple-instance learning with contrastive multi-view representation for static Windows PE malware detection,” Computers, Materials and Continua, 2026, doi: 10.32604/cmc.2026.084268.
[11] A. Mester, Z. Bodó, P. Vinod, and M. Conti, “Towards a Malware Family Classification Model Using Static Call Graph Instruction Visualization,” in Lecture Notes in Computer Science, Springer Nature Singapore, 2025, pp. 167–186. doi: 10.1007/978-981-96-3531-3_9.
[12] I. Almomani, A. Alkhayer, and W. El-Shafai, “E2E-RDS: Efficient end-to-end ransomware detection system based on static-based ML and vision-based DL approaches,” Sensors, 2023, doi: 10.3390/s23094467.
[13] Y. Wu, Y. Liu, Z. Zhang, and others, “A swarm intelligence-enhanced ransomware detection framework via dynamic memory feature optimization,” Expert Syst. Appl., 2026, doi: 10.1016/j.eswa.2025.129225.
[14] M. Cen, F. Jiang, and R. Doss, “RansoGuard: A RNN-based framework leveraging pre-attack sensitive APIs for early ransomware detection,” Computers & Security, vol. 150, p. 104293, 2025, doi: 10.1016/j.cose.2024.104293.
[15] P. M. Anand, P. V. S. Charan, H. Chunduri, and S. K. Shukla, “LARM: Linux anti ransomware monitor,” Comput. Secur., 2025, doi: 10.1016/j.cose.2025.104700.
[16] J. A. Gómez-Hernández and P. García-Teodoro, “Lightweight crypto-ransomware detection in Android based on reactive honeyfile monitoring,” Sensors, 2024, doi: 10.3390/s24092679.
[17] Y. Zhang, W. Ren, T. Zhu, and Y. Ren, “SaaS: A situational awareness and analysis system for massive Android malware detection,” Future Generation Computer Systems, 2019, doi: 10.1016/j.future.2018.12.028.
[18] A. Mahboubi, S. Camtepe, K. Ansari, and others, “Shared file protection against unauthorised encryption using a buffer-based signature verification method,” Journal of Information Security and Applications, 2024, doi: 10.1016/j.jisa.2024.103873.
[19] G. Arányi, T. Miseta, and V. Szücs, “Ransomware detection based on server-side file operation logs using machine learning,” Journal on Information Security, vol. 2026, no. 1, 2026, doi: 10.1186/s13635-026-00229-7.
[20] G. Hu, F. Chen, and J. Shao, “TDMRans: Toward a two-stage detection method of ransomware encryption behavior in storage system,” IEEE Trans. Netw. Sci. Eng., 2026, doi: 10.1109/TNSE.2026.3719148.
[21] P. Bhandary and C. Nicholas, “Temporal behavioral archetypes of ransomware in Active Directory environments,” in Proc. Int. Symp. Digital Forensics and Security (ISDFS), 2026. doi: 10.1109/ISDFS69419.2026.11459079.
[22] K. Selvaraj, M. M. Mahinderjit Singh, and Z. F. Zaaba, “HARVEST: Hardware-based ransomware detection and stage tracking for AIoMT devices,” Journal of Network and Computer Applications, 2026, doi: 10.1016/j.jnca.2026.104458.
[23] Y. Almasri, M. D. S. Islam, M. Elnour, and others, “An optimized latent-space classifier with Banzhaf-inspired probabilistic feature selection for ransomware detection in IoT edge environments,” Results in Engineering, 2026, doi: 10.1016/j.rineng.2026.111989.
[24] G. M. and S. C. Sethuraman, “A comprehensive survey on deep learning based malware detection techniques,” Comput. Sci. Rev., vol. 47, p. 100529, 2023, doi: 10.1016/j.cosrev.2022.100529.
[25] S. Kurmambayev, S. Amanzholova, and H. M. Rai, “A comparative study of supervised machine learning algorithms for ransomware detection,” in Proc. 2026 IEEE 6th Int. Conf. Smart Information Systems and Technologies (SIST), 2026. doi: 10.1109/SIST61674.2026.11596349.
[26] N. Balram, G. Hsieh, and C. McFall, “Static malware analysis using machine learning algorithms on APT1 dataset with string and PE header features,” in Proc. 6th Annu. Conf. Computational Science and Computational Intelligence (CSCI), 2019. doi: 10.1109/CSCI49370.2019.00022.
[27] O. Shinde, A. Khobragade, and P. Agrawal, “Static malware detection of Ember windows-PE API call using machine learning,” in AIP Conference Proceedings, AIP Publishing, 2023, p. 020001. doi: 10.1063/5.0130256.
[28] D. Gibert, J. Planes, C. Mateu, and Q. Le, “Fusing feature engineering and deep learning: A case study for malware classification,” Expert Syst. Appl., 2022, doi: 10.1016/j.eswa.2022.117957.
[29] A. Hussain, A. Saadia, M. Alhussein, and others, “Enhancing ransomware defense: Deep learning-based detection and family-wise classification of evolving threats,” PeerJ Comput. Sci., 2023, doi: 10.7717/peerj-cs.2546.
[30] A. M. Sharaf, S. A. Al-Azazi, and M. A. Saeed, “Behavioral Memory-Artifact Deep Learning for Ransomware Detection with Confidence-Aware Automated Response,” in 2026 6th International Conference on Emerging Smart Technologies and Applications (eSmarTA), IEEE, 2026, pp. 1–8. doi: 10.1109/esmarta70636.2026.11652256.
[31] T. W. A. Putera, A. Bramantoro, R. Ramlie, and S. H. M. Ali, “CNN-Based Ransomware Detection in the RANSAP Dataset Using Storage Access Patterns,” in 2025 7th International Conference on Applied Computational Intelligence in Information Systems (ACIIS), IEEE, 2025, pp. 1–6. doi: 10.1109/aciis66255.2025.11402967.
[32] M. E. Ahmed, H. Kim, S. Camtepe, and S. Nepal, “Peeler: Profiling kernel-level events to detect ransomware,” in Lecture Notes in Computer Science, 2021. doi: 10.1007/978-3-030-88418-5_12.
[33] S. Mehnaz, A. Mudgerikar, and E. Bertino, “RWGuard: A real-time detection system against cryptographic ransomware,” in Lecture Notes in Computer Science, 2018. doi: 10.1007/978-3-030-00470-5_6.
[34] S. Sheen, K. A. Asmitha, and S. Venkatesan, “R-Sentry: Deception based ransomware detection using file access patterns,” Computers and Electrical Engineering, vol. 103, p. 108346, 2022, doi: 10.1016/j.compeleceng.2022.108346.
[35] M. A. Putrevu, V. S. C. Putrevu, and S. K. Shukla, “Early detection of ransomware activity based on hardware performance counters,” in ACM Int. Conf. Proceeding Series, 2023. doi: 10.1145/3579375.3579377.
[36] K. S. Vinesh and K. Devi, “Identifying network traffic patterns associated with ransomware targeting data in transit,” in Proc. 4th IEEE Int. Conf. Interdisciplinary Approaches in Technology and Management for Social Innovation (IATMSI), 2026. doi: 10.1109/IATMSI68868.2026.11465711.
[37] C. Lamprecht and J. Chavula, “Deep learning for ransomware detection in encrypted traffic,” in Proc. 2nd Cybersecurity for Development Conf. (C4D), 2025. doi: 10.1109/C4D65382.2025.11306467.
[38] Z. Almulla, M. Alamri, and M. Frikha, “Intrusion detection system for ransomware in network traffic using supervised machine learning,” International Journal of Advanced Computer Science and Applications, 2026, doi: 10.14569/IJACSA.2026.0170581.
[39] A. O. Almashhadani, D. Carlin, M. Kaiiali, and S. Sakir Sezer, “MFMCNS: A multi-feature and multi-classifier network-based system for ransomworm detection,” Comput. Secur., 2022, doi: 10.1016/j.cose.2022.102860.
[40] P. Yan, T. T. Khoei, R. S. Hyder, and R. S. Hyder, “A dual-stage ensemble approach to detect and classify ransomware attacks,” in Proc. IEEE 15th Annu. Ubiquitous Computing, Electronics and Mobile Communication Conf. (UEMCON), 2024. doi: 10.1109/UEMCON62879.2024.10754695.
[41] M. Almousa, J. Osawere, and M. Anwar, “Identification of ransomware families by analyzing network traffic using machine learning techniques,” in Proc. 3rd Int. Conf. Transdisciplinary AI (TransAI), 2021. doi: 10.1109/TransAI51903.2021.00012.
[42] A. Vitale, K. van Liebergen, J. Caballero, and others, “Family ties: A close look at the influence of static features on the precision of malware family clustering,” in Proc. eCrime Researchers Summit, 2025. doi: 10.1109/eCrime66972.2025.11327864.
[43] G. Barnes and A. Ghafarian, “Machine learning-based static ransomware detection using PE header features and SHAP interpretation,” Journal of Cybersecurity and Privacy, 2026, doi: 10.3390/jcp6020058.
[44] D. Vaishnavi, R. Rajakumar, S. RanjeethKumar, and M. Anuradha, “Optimal Machine Learning Model to Detect Ransomware on Processor and Disk,” in 2024 International Conference on IoT Based Control Networks and Intelligent Systems (ICICNIS), IEEE, 2024, pp. 1296–1303. doi: 10.1109/icicnis64247.2024.10823178.
[45] A. AlMajali, W. Dweik, Y. Abdelghafur, and others, “Detecting ransomware through dynamic API call monitoring and machine learning,” Applied Sciences, 2026, doi: 10.3390/app16115232.
[46] C. C. Moreira, D. C. Moreira, and C. D. S. D. Sales, “Improving ransomware detection based on portable executable header using Xception convolutional neural network,” Comput. Secur., 2023, doi: 10.1016/j.cose.2023.103265.
[47] T.-L. Lin, H.-Y. Chang, Y.-Y. Chiang, and others, “Ransomware detection by distinguishing API call sequences through LSTM and BERT models,” Comput. J., 2024, doi: 10.1093/comjnl/bxad005.
[48] C. C. Moreira, D. C. Moreira, and C. Sales, “A comprehensive analysis combining structural features for detection of new ransomware families,” Journal of Information Security and Applications, 2024, doi: 10.1016/j.jisa.2024.103716.
[49] R. Kumar and G. Subbiah, “Zero-day malware detection and effective malware analysis using Shapley ensemble boosting and bagging approach,” Sensors, 2022, doi: 10.3390/s22072798.
[50] M. Mimura, “Evaluation of printable character-based malicious PE file-detection method,” Internet of Things, 2022, doi: 10.1016/j.iot.2022.100521.
[51] B. Yuan, J. Wang, D. Liu, and others, “Byte-level malware classification based on Markov images and deep learning,” Comput. Secur., 2020, doi: 10.1016/j.cose.2020.101740.
[52] S. Gulmez, A. Kakişim, and I. Soğukpinar, “XRan: Explainable deep learning-based ransomware detection using dynamic analysis,” Comput. Secur., 2024, doi: 10.1016/j.cose.2024.103703.
[53] S. Meti, V. Sidramayyanmath, S. Patil, and P. Patil, “Ransomware detection using machine learning and explainable AI,” in Lecture Notes in Networks and Systems, 2025. doi: 10.1007/978-981-96-1918-4_3.
[54] C. Wang, Z. Qin, J. Zhang, and H. Yin, “A malware variants detection methodology with an opcode based feature method and a fast density based clustering algorithm,” in Proc. 12th Int. Conf. Natural Computation, Fuzzy Systems and Knowledge Discovery (ICNC-FSKD), 2016. doi: 10.1109/FSKD.2016.7603221.
[55] H. Zhang, X. Xiao, F. Mercaldo, and others, “Classification of ransomware families with machine learning based on N-gram of opcodes,” Future Generation Computer Systems, 2019, doi: 10.1016/j.future.2018.07.052.
[56] A. G. Kakişim, S. Gulmez, and I. Soğukpinar, “Sequential opcode embedding-based malware detection method,” Computers and Electrical Engineering, 2022, doi: 10.1016/j.compeleceng.2022.107703.
[57] Y. A. Ahmed, B. Koçer, S. Huda, and others, “A system call refinement-based enhanced minimum redundancy maximum relevance method for ransomware early detection,” Journal of Network and Computer Applications, 2020, doi: 10.1016/j.jnca.2020.102753.
[58] B. M. Khammas, “Ransomware detection using random forest technique,” ICT Express, 2020, doi: 10.1016/j.icte.2020.11.001.
[59] R. Islam, R. Tian, L. M. Batten, and S. Versteeg, “Classification of malware based on integrated static and dynamic features,” Journal of Network and Computer Applications, 2013, doi: 10.1016/j.jnca.2012.10.004.
[60] O. A. Madamidola, F. Ngobigha, and A. Ez-Zizi, “Detecting new obfuscated malware variants: A lightweight and interpretable machine learning approach,” Intelligent Systems with Applications, 2025, doi: 10.1016/j.iswa.2024.200472.
[61] Y. K. Sharma, D. S. Tomar, R. K. Pateriya, and S. Bhandari, “MOSDroid: Obfuscation-resilient Android malware detection using multisets of encoded opcode sequences,” Comput. Secur., 2025, doi: 10.1016/j.cose.2025.104379.
[62] V. A. Monsalve Obregon, J. P. Rios Diaz, and C. M. Torres Paredes, “Ransomware Detection Using Executable Header Features and Machine Learning Techniques,” in Proceedings of the 2025 8th International Conference on Systems Engineering - Cybersecurity & AI: Building a reliable digital future, ACM, 2025, pp. 87–97. doi: 10.1145/3771678.3771690.
[63] S. Aurangzeb, R. N. B. Rais, M. Aleem, M. A. Islam, and M. A. Iqbal, “On the classification of Microsoft-Windows ransomware using hardware profile,” PeerJ Comput. Sci., vol. 7, p. e361, 2021, doi: 10.7717/peerj-cs.361.
[64] H. Gunduz, “Malware detection framework based on graph variational autoencoder extracted embeddings from API-call graphs,” PeerJ Comput. Sci., vol. 8, p. e988, 2022, doi: 10.7717/peerj-cs.988.
[65] X. Gao, C. Hu, C. Shan, and W. Han, “MaliCage: A packed malware family classification framework based on DNN and GAN,” Journal of Information Security and Applications, vol. 68, p. 103267, 2022, doi: 10.1016/j.jisa.2022.103267.
[66] J. Leng, T. Li, and W. Xu, “PE Malware Detection via Optimized Static Features and Ensemble Learning,” Concurr. Comput., vol. 38, no. 9, 2026, doi: 10.1002/cpe.70732.
[67] M. S. Abbasi, H. Al-Sahaf, M. Mansoori, and I. Welch, “Behavior-based ransomware classification: A particle swarm optimization wrapper-based approach for feature selection,” Appl. Soft Comput., vol. 121, p. 108744, 2022, doi: 10.1016/j.asoc.2022.108744.
[68] N. A. Abu-Taleb et al., “A Proactive Ransomware Detection System for Windows Based on File System Behavior Analysis and Unsupervised Deep Learning,” in 2026 6th International Conference on Emerging Smart Technologies and Applications (eSmarTA), IEEE, 2026, pp. 1–6. doi: 10.1109/esmarta70636.2026.11652249.
[69] S. M. Z. Javed, M. F. Amjad, S. Tahir, and S. Ali, “Attention-Enhanced CNN–BiLSTM Framework for Dynamic Behavior-Based Ransomware Family Classification,” in 2025 IEEE 22nd International Conference on Smart Communities: Improving Quality of Life using AI, Robotics and IoT (HONET), IEEE, 2025, pp. 195–200. doi: 10.1109/honet67928.2025.11318420.
[70] I. Ku, I. Jeong, and S. Han, “RansomFisher: Behavior-based ransomware detection without decoys,” ICT Express, vol. 12, no. 4, pp. 894–898, 2026, doi: 10.1016/j.icte.2026.06.002.
[71] A. Alqahtani, M. O. Ohemeng, and F. T. Sheldon, “An Intelligent Sensing Framework for Early Ransomware Detection Using MHSA-LSTM Machine Learning,” Sensors, vol. 26, no. 3, p. 952, 2026, doi: 10.3390/s26030952.
[72] P. M. Anand, P. V. S. Charan, H. Chunduri, and S. K. Shukla, “RANDART: A Hybrid Approach Leveraging File Traps and Registry Monitoring to Thwart Crypto Ransomware on Windows Endpoints,” in 2025 IEEE/ACM 6th International Workshop on Engineering and Cybersecurity of Critical Systems (EnCyCriS), IEEE, 2025, pp. 15–22. doi: 10.1109/encycris66464.2025.00009.
[73] A. Pomsathit, “Interpretable Pre-Ransomware Detection for SOCs Using SHAP and Lightweight ML,” IEEE Access, pp. 1–1, 2026, doi: 10.1109/access.2026.3730303.
[74] P. Shailaja, T. Jahan, K. Sharmila, P. B. S. Varma, S. Arra, and P. M. Kumar, “MalwareNet: an intelligent malware detection and classification using advanced extreme leaning machine in edge computing environment,” Egyptian Informatics Journal, vol. 31, p. 100714, 2025, doi: 10.1016/j.eij.2025.100714.
[75] D. W. Fernando and N. Komninos, “FeSAD ransomware detection framework with machine learning using adaption to concept drift,” Computers & Security, vol. 137, p. 103629, 2024, doi: 10.1016/j.cose.2023.103629.
[76] S. Jawad and H. M. Ahmed, “Online ransomware detection with the enhancing implementation using JAYA and TLBO algorithms,” in AIP Conference Proceedings, AIP Publishing, 2026, p. 040107. doi: 10.1063/5.0330436.
[77] A. Patel, D. S. Tomar, R. K. Pateriya, and R. Haripriya, “Mitigating concept drift in malware classification: A temporal and resource-aware evaluation,” Knowl. Based. Syst., vol. 350, p. 116534, 2026, doi: 10.1016/j.knosys.2026.116534.
[78] H. Kabuye, B. Issac, and N. Jeyamohan, “Agentic SABRE: An uncertainty-aware neuro-symbolic multi-agent framework for adaptive ransomware detection,” Expert Syst. Appl., vol. 332, p. 133558, 2027, doi: 10.1016/j.eswa.2026.133558.
[79] A. Brown, M. Gupta, and M. Abdelsalam, “Automated machine learning for deep learning based malware detection,” Computers & Security, vol. 137, p. 103582, 2024, doi: 10.1016/j.cose.2023.103582.
[80] M. Geden and J. Happa, “Classification of Malware Families Based on Runtime Behaviour,” in Lecture Notes in Computer Science, Springer International Publishing, 2018, pp. 33–48. doi: 10.1007/978-3-030-01689-0_3.
[81] E. J. Khalefa and D. A. A. Salman, “Attribution classification method of advanced persistent threat (APT) malware using AI learning,” International Journal on Technical and Physical Problems of Engineering, 2023, [Online]. Available: https://www.scopus.com/pages/publications/85153759661
[82] S. Dambra et al., “Decoding the Secrets of Machine Learning in Malware Classification: A Deep Dive into Datasets, Feature Extraction, and Model Performance,” in Proceedings of the 2023 ACM SIGSAC Conference on Computer and Communications Security, ACM, 2023, pp. 60–74. doi: 10.1145/3576915.3616589.
[83] V. R. and S. K.P., “DeepMalNet: Evaluating shallow and deep networks for static PE malware detection,” ICT Express, vol. 4, no. 4, pp. 255–258, 2018, doi: 10.1016/j.icte.2018.10.006.
[84] U. Ahmed, J. C.-W. Lin, and G. Srivastava, “Mitigating adversarial evasion attacks of ransomware using ensemble learning,” Computers and Electrical Engineering, vol. 100, p. 107903, 2022, doi: 10.1016/j.compeleceng.2022.107903.
[85] F. C. Onwuegbuche, S. O. Adelodun, A. D. Jurcut, and L. Pasquale, “MLRan: A behavioural dataset for ransomware analysis and detection,” Journal of Network and Computer Applications, vol. 250, p. 104475, 2026, doi: 10.1016/j.jnca.2026.104475.
[86] V. S. Vivek, V. Lokesh, T. Kaushik, U. Kumaran, B. Umah, and G. G. Devarajan, “Ransome Ware Detection Using Machine Learning and Deep Learning Models,” in Lecture Notes in Networks and Systems, Springer Nature Singapore, 2025, pp. 105–117. doi: 10.1007/978-981-97-8946-7_8.
[87] K. Meechanchuang, P. Sitsaengchai, K. Bowornsujaritkul, S. Tritilanunt, and T. Phienthrakul, “Evaluating the Efficacy of Machine Learning Techniques in Ransomware Detection,” in 2025 22nd International Joint Conference on Computer Science and Software Engineering (JCSSE), IEEE, 2025, pp. 209–216. doi: 10.1109/jcsse67377.2025.11297864.
[88] Y. Qiao, N. B. Sathyanarayana, C. Shi, Z. He, T. Wang, and T. Hou, “A survey on adversarial machine learning: Attacks, defenses, real-world applications, and future research directions,” Neurocomputing, vol. 671, p. 132670, 2026, doi: 10.1016/j.neucom.2026.132670.
[89] Y. Xu, Y. Fang, Y. Xu, and Z. Wang, “Automatic optimization for generating adversarial malware based on prioritized evolutionary computing,” Appl. Soft Comput., vol. 173, p. 112933, 2025, doi: 10.1016/j.asoc.2025.112933.
[90] V. Sihag, M. Vardhan, and P. Singh, “BLADE: Robust malware detection against obfuscation in android,” Forensic Science International: Digital Investigation, vol. 38, p. 301176, 2021, doi: 10.1016/j.fsidi.2021.301176.
Downloads
Published
Issue
Section
License
Copyright (c) 2026 Al-Noor Journal of Engineering Management and Computer Science

This work is licensed under a Creative Commons Attribution-NonCommercial-ShareAlike 4.0 International License.
How to Cite